CarelineOS (Backend)
Scalable backend for digital health: APIs (TODO: verify count) supporting appointments, patient records, role-based access, and secure workflows. Node.js, MongoDB, modular architecture for hospital and clinic management.
Case study summary
- Client type
- Health-tech startup
- Industry
- Healthcare
- Duration
- TODO: Confirm project dates and duration
- My role
- Backend API developer
- Team size
- TODO: Confirm team size and collaborators
- Stack
- Node.js, Express, MongoDB, REST API, JWT
- Platforms
- Backend services
Challenge
Give the health platform a stable service layer for identity, appointments and patient data while keeping role permissions consistent.
Approach
Separate domain services, define request contracts and enforce resource access before reading or changing stored records.
Architecture
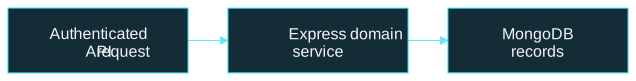
Key features
- Domain-oriented REST APIs
- Role-based access
- Appointment operations
- Data model integration
Results and measurement
The delivered scope is described in this case study. Numeric performance or business results require a measurement source and owner approval.
TODO: Add the verified baseline, final value, measurement period and evidence link. API-count claim: TODO — verify before publication.
Client feedback
TODO: Add an approved client quote for this project, with the client's attribution and source. No invented testimonial is displayed.
Want something similar? Explore this service →Project at a glance
My contribution and the engineering challenge
- My role
- Backend API development
- The problem
- Give the health platform a consistent API contract across users, appointments, patient data and analytics.
What I delivered
- Node.js/Express REST services
- MongoDB data models
- Authentication and role-based API access
How the parts connect
- STEP 1Authenticated request
- STEP 2Domain service and access checks
- STEP 3MongoDB records
Simplified implementation overview.
A key design decision
Separate API domains so frontend work can depend on explicit contracts rather than application internals.
TODO: Add permission-approved, sanitized product screenshots. Concept art is not shown as product evidence.
Technical concept illustration. The case study below describes the project implementation.
Why This Was Hard
A hospital platform can't afford sloppy API design. Patient data is sensitive, roles are strict, and downtime or data leakage isn't an option. This is the backend powering CarelineOS — a modular REST API layer handling every digital-health operation across hospitals, clinics, and multi-tenant deployments — and it needed clear domain boundaries (auth, users, appointments, analytics) so the surface area stayed manageable even as the API count grew past APIs (TODO: verify count). Where the CarelineOS app project covers the product experience, this is the engine underneath it.
What I Built
- APIs (TODO: verify count) covering appointments, patient records, vitals, and messaging
- Role-based access control — admin, doctor, patient, and staff permission guards enforced at the API layer, not just the UI
- Secure workflows — encrypted communication channels and audit trails for sensitive actions
- Modular domain architecture — auth, users, appointments, and analytics kept as separate, independently testable modules
- Optimized MongoDB models — indexed queries built for the access patterns a hospital dashboard actually uses (recent vitals, upcoming appointments, per-doctor patient lists)
- Refresh-token auth flow — short-lived access tokens with secure refresh handling
Tech Stack
- Runtime: Node.js
- Framework: Express
- Database: MongoDB
- Auth: JWT, refresh tokens
Key Decisions
- Structured the API around domain modules (auth, users, appointments, analytics) instead of one flat routes file, so a new engineer could find and extend a single domain without reading the whole backend
- Used short-lived access tokens with a separate refresh flow rather than long-lived JWTs, trading a bit of extra request overhead for a meaningfully smaller attack window on sensitive patient data
- Indexed MongoDB collections around the queries the dashboard actually runs (recent vitals per patient, upcoming appointments per doctor) rather than indexing everything, keeping write performance predictable as data grew
- Documented every endpoint's contract before the frontend team built against it, treating the API surface as a product in its own right
Outcome
A production-ready backend supporting the full CarelineOS platform, with clear API contracts and documentation that let the frontend team build against a stable, predictable interface.
Related work
CarelineOS (App)
Full-stack digital health platform for hospitals, clinics, doctors, and patients. MUI frontend, Node.js backend, MongoDB. APIs (TODO: verify count), role-based access (admin, doctor, patient, staff), analysis dashboard for vitals, and secure doctor–patient communication.
MatchCircuit
REST API backend for a dating app: profile management, match-making logic, and real-time chat. Node.js, Express, and MongoDB power matching, messaging, and moderation at scale.
StoreParity
Full-stack seller-operations dashboard with 100% feature parity against a leading marketplace's seller console. Responsive React frontend and admin panel with category management, articles, and localization. Express backend with MongoDB. Built and tested via RDP as the reference service is unavailable in Pakistan.
Interested in similar work?
Review my services and how we can define a useful first milestone.
Discuss similar work